
Do AI Scribes Need a Business Associate Agreement? Yes, but a BAA Isn’t Enough
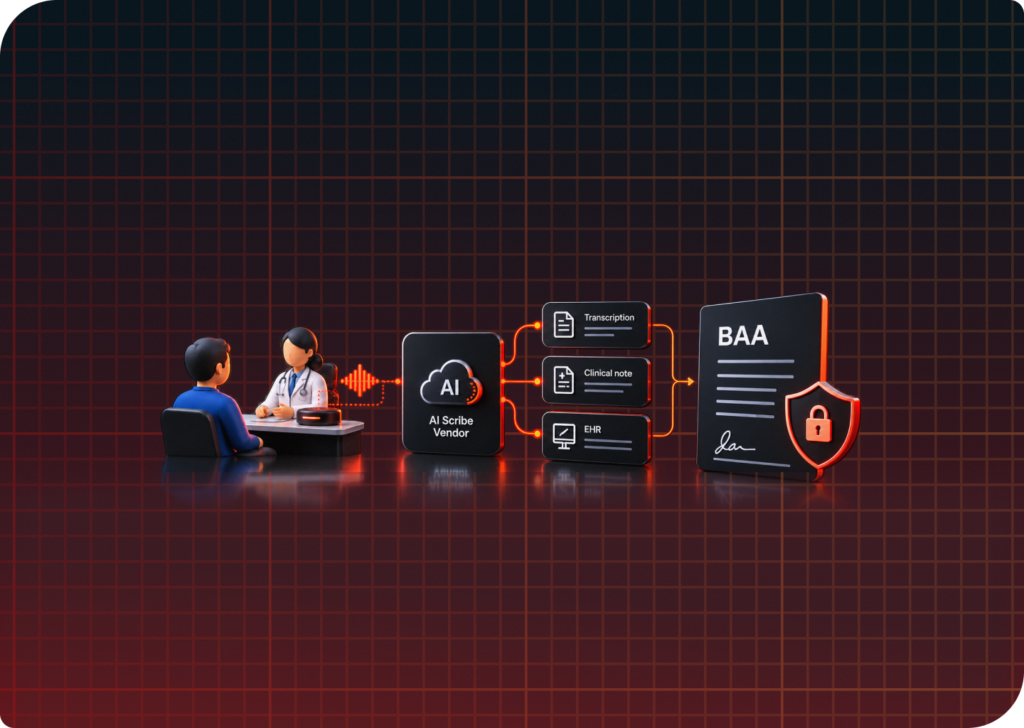
Do AI scribes need a business associate agreement? Yes, almost always. If the scribe hears real patients, the vendor handles PHI, so sign before the first visit, even on a free trial. “We delete the audio” won’t save you. A strong BAA covers audio retention, wrong chart notes, and EHR access. But consent laws and untested security still leave you exposed.
How to Get SOC 2 Type II and HIPAA Compliance Right for Telehealth Vendors
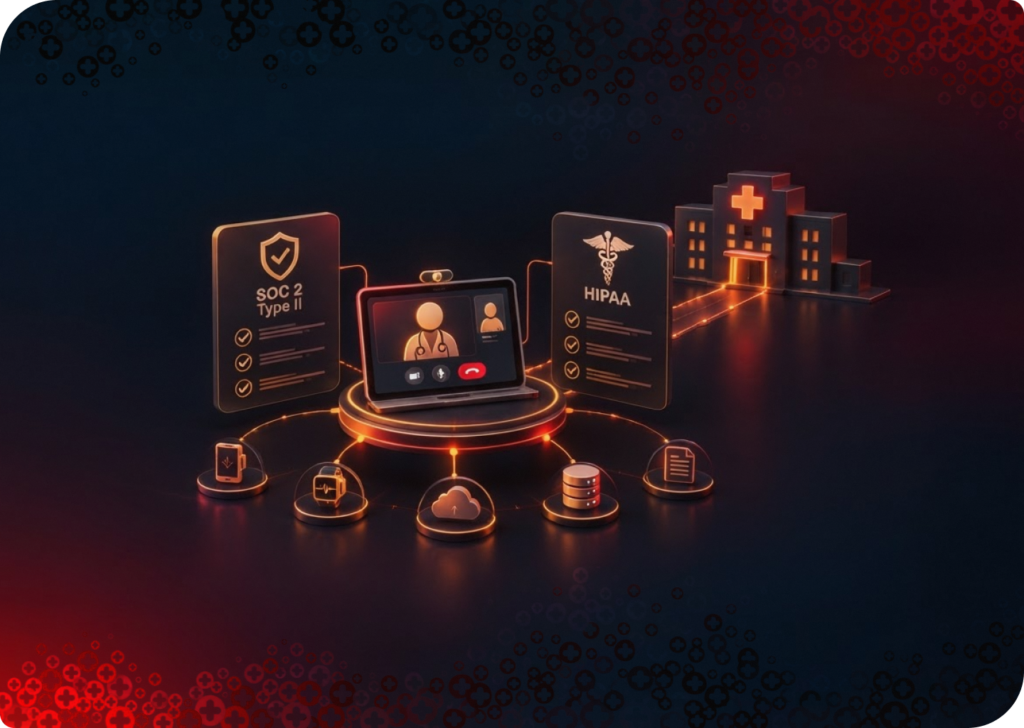
For telehealth vendors, SOC 2 Type II and HIPAA compliance are critical to passing hospital security reviews and securing contracts. But hospitals look beyond audit reports. They examine how your platform protects patient data, manages video recordings, handles AI tools, and controls third-party access. This guide explains what hospitals and auditors actually check, how SOC 2 and HIPAA requirements overlap, and how to prepare for both without duplicating compliance efforts.
How to Perform Application Security Gap Assessment: 6 Steps
A penetration test can uncover vulnerabilities, but it may miss the security gaps that allow them to recur. This guide explains how to perform an application security gap assessment in six steps, from evaluating security controls and development practices to prioritizing risks and fixing their root causes. With practical examples from healthcare applications, it also covers the tools, evidence, and frameworks needed to keep applications secure across releases.
HIPAA Compliant AEO Attribution: Win AI Search Without PHI Risk
Every time your healthcare brand appears in AI answers, patient data get leaks through the tools that helped it get there. Tracking pixels, AI writing tools, chatbots, and search monitoring platforms can expose PHI without ever publishing it. HIPAA compliant AEO requires securing the tools and workflows behind those AI search visibility.
HIPAA Compliance for Healthcare Startups in the Research Triangle Park: A 2026 Guide
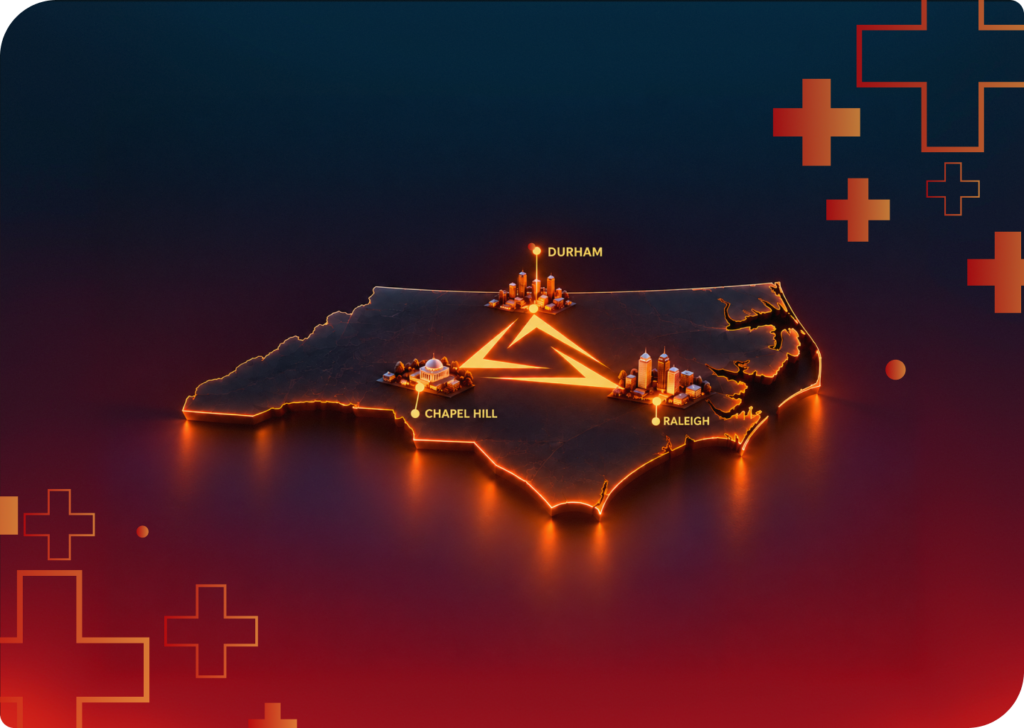
For healthcare startups in Research Triangle Park, North Carolina, HIPAA compliance does not always end with determining whether you are a covered entity or business associate. If you handle sensitive patient information, state privacy duties may still apply. The strongest approach to HIPAA compliance for healthcare startups is to map where patient data flows, assess risks regularly, review vendors carefully, and update controls whenever your systems or workflows change.
How Does KLEAP Help with Your HIPAA, HITRUST or SOC 2 Compliance in Healthcare?
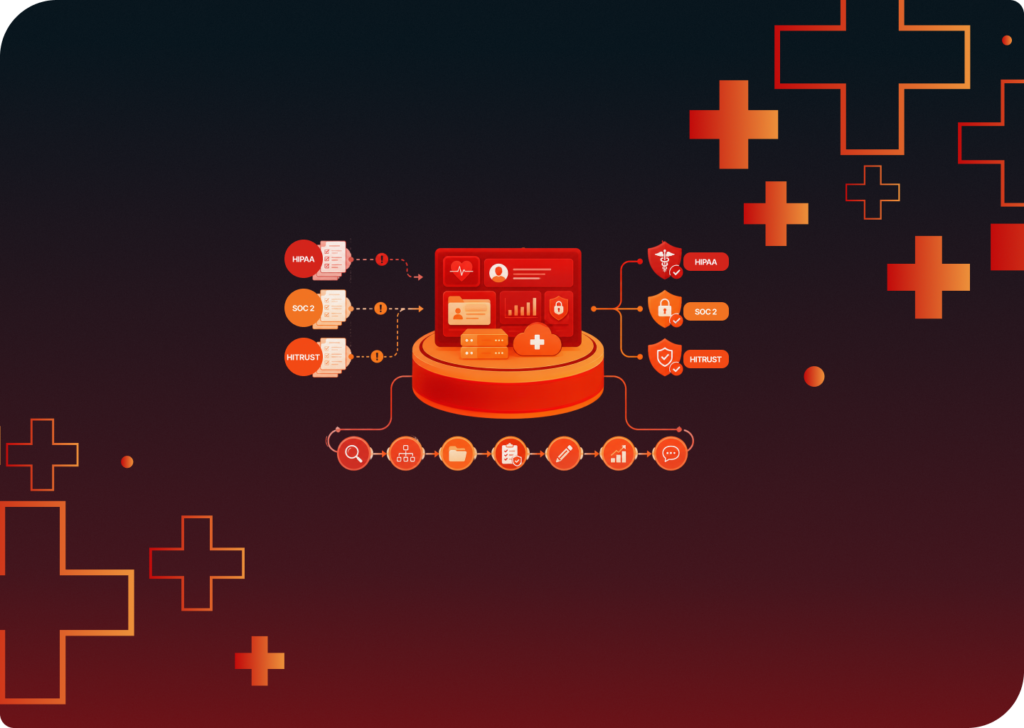
In this blog, we compare HIPAA, SOC 2, and HITRUST, answer the sequencing and audit-prep questions healthcare startups ask us most, and explain how KLEAP scopes requirements, assesses vendor risk, and closes gaps through manual penetration testing before an audit or a procurement review.
5 Questions to Ask the SaaS Vendor Before Signing a Healthcare BAA
Most healthcare BAA gets signed at the bare legal minimum and filed away. This blog breaks down five diligence questions, covering data location, AI training use, termination, security proof, and breach notification speed, everything that turn a BAA from paperwork into enforced vendor accountability, before a breach forces the issue.
7 Major Healthcare Cybersecurity Breaches in the U.S. (2026)
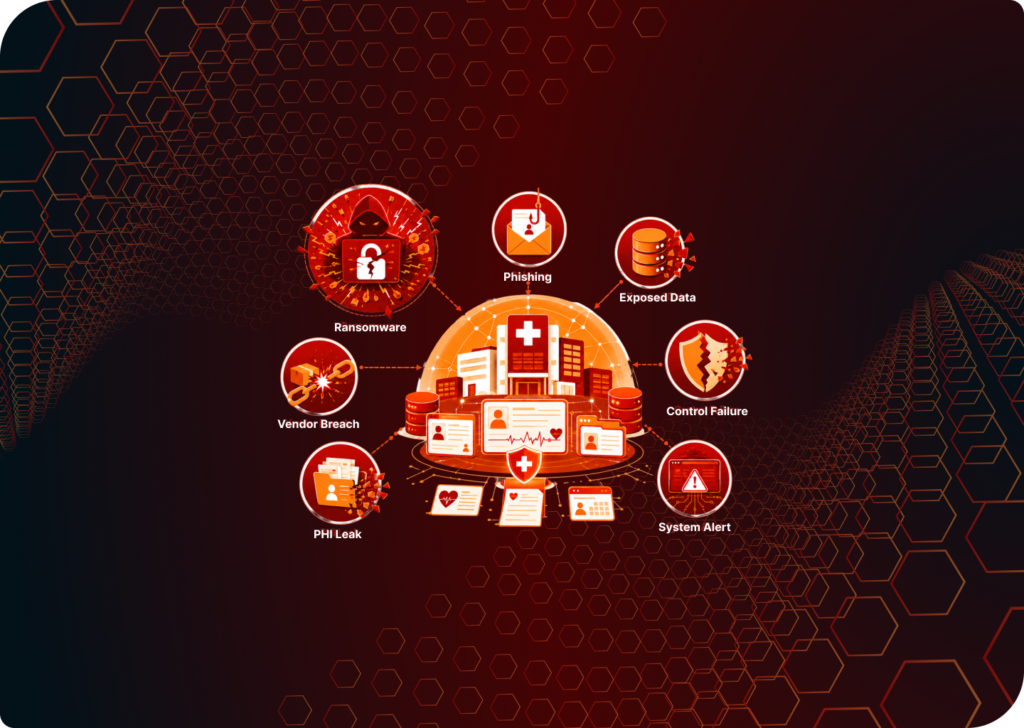
Explore seven major healthcare cybersecurity breaches in the United States, including Change Healthcare, Anthem, HCA Healthcare, Kaiser Permanente, and Ascension. See what these healthcare security breach examples reveal about stolen credentials, weak access controls, third-party risk, poor data visibility, and recovery gaps, and what healthcare organizations can learn from these major healthcare security breaches in 2026.
HIPAA Compliant AI in Healthcare: What Healthcare Security Teams Need to Check Before Deployment in 2026
Healthcare teams can use AI tools and LLMs with PHI in a HIPAA-compliant way. But in 2026, AI HIPAA compliance depends on the deployment, not the model name or vendor claim. This guide explains how to evaluate HIPAA compliant AI tools, BAAs, data flows, access controls, model training, retention, third-party providers, and EMR integration with AI medical assistants before patient data enters the workflow.
Manual Penetration Testing for Healthcare SOC 2 Type II
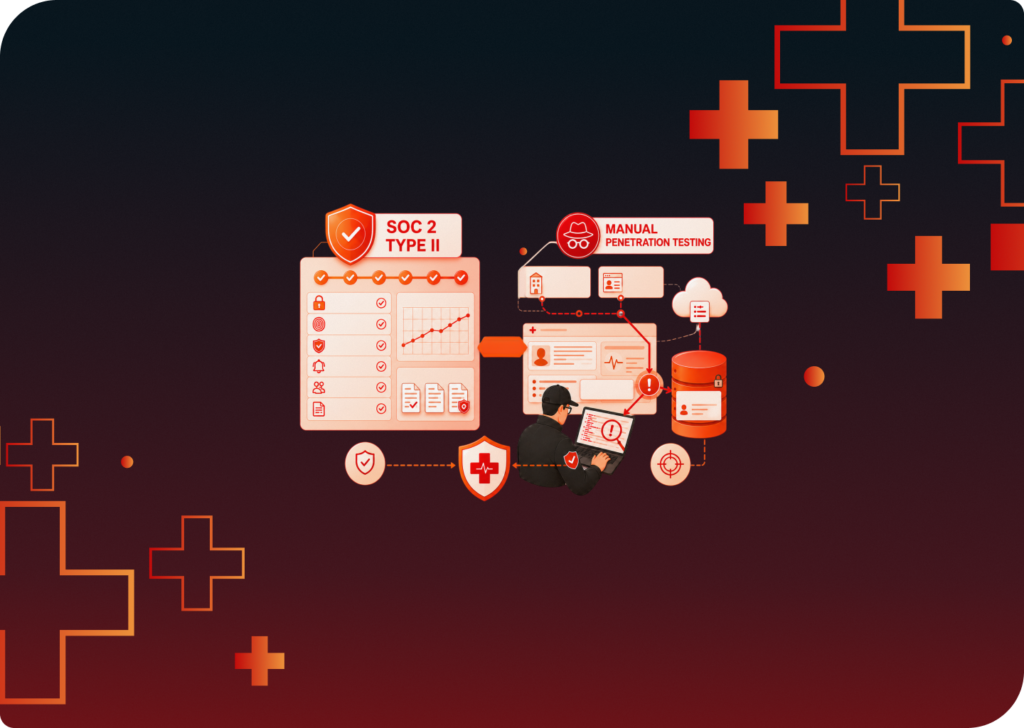
A clean SOC 2 Type II report attests your controls operated, but not that they actually stop an attacker. The gaps that leak PHI, like broken access control and business logic abuse, are exactly what automated scans miss. Here’s how manual penetration testing in SOC 2 finds those gaps and strengthens your healthcare SOC 2 evidence.