
Prioritization Between HITRUST, HIPAA & SOC 2 For Healthcare Startups
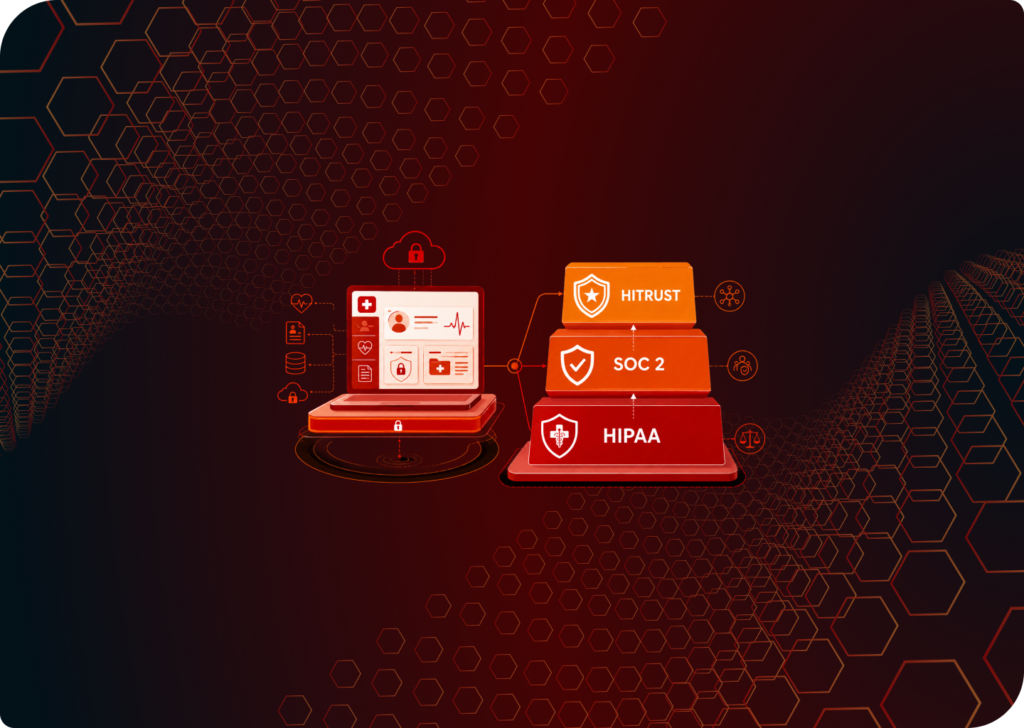
Startups have to think about preparing for HIPAA, HITRUST, and SOC 2 together, not individually. This guide explains how the three frameworks overlap and diverge, what SOC 2 Type II requires, when HITRUST is worth it, and how to sequence them so that you don’t have to pull off triple the amount of work.
SOC 2 vs HIPAA: What’s Different, What Overlaps & Do You Need Both?
SOC 2 vs HIPAA is not an either-or decision. SOC 2 can cover much of the security work HIPAA requires, but it does not establish HIPAA compliance. Organizations that need both should reuse shared controls and evidence, then focus their effort on the HIPAA-specific gaps that SOC 2 leaves behind.
Why Manual Penetration Testing Supports Your ISO 27001 Compliance Program
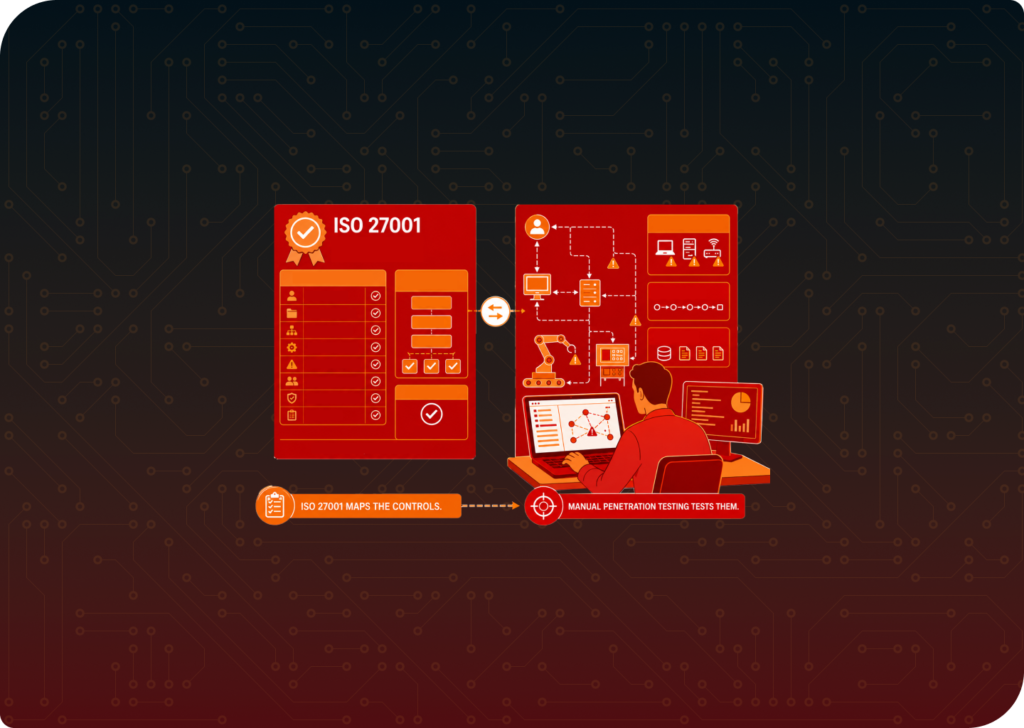
An ISO 27001 compliance certificate tells how well you manage your information security. It does not tell you whether an attacker can get in. This blog breaks down how ISO 27001 penetration testing is relevant, what auditors actually expect, and why manual testing is non-negotiable for compliance evidence.
HIPAA Compliance Requirements for Digital Health Startups
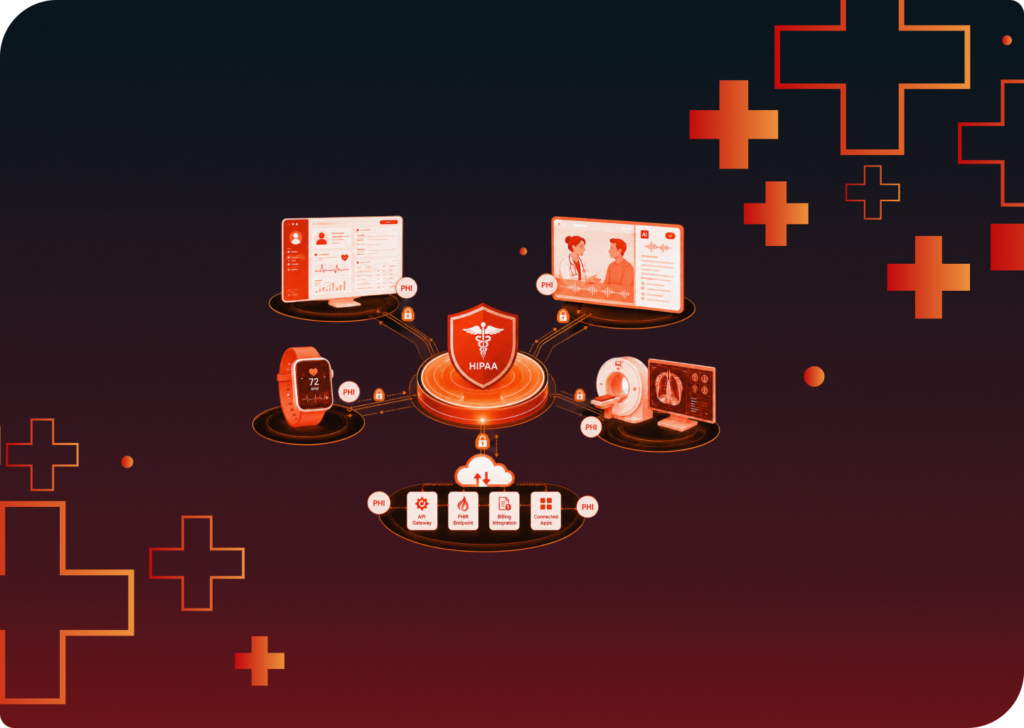
Digital health startups are increasingly becoming integrated in healthcare. But the focus is more on the engineering side than on compliance. As a result, startups are facing data breaches that are becoming more costly. Whether your product is EHR, imaging, AI scribing, or wearables, this blog will guide you through HIPAA’s compliance requirements.
BAA for HIPAA Compliant AI in Healthcare
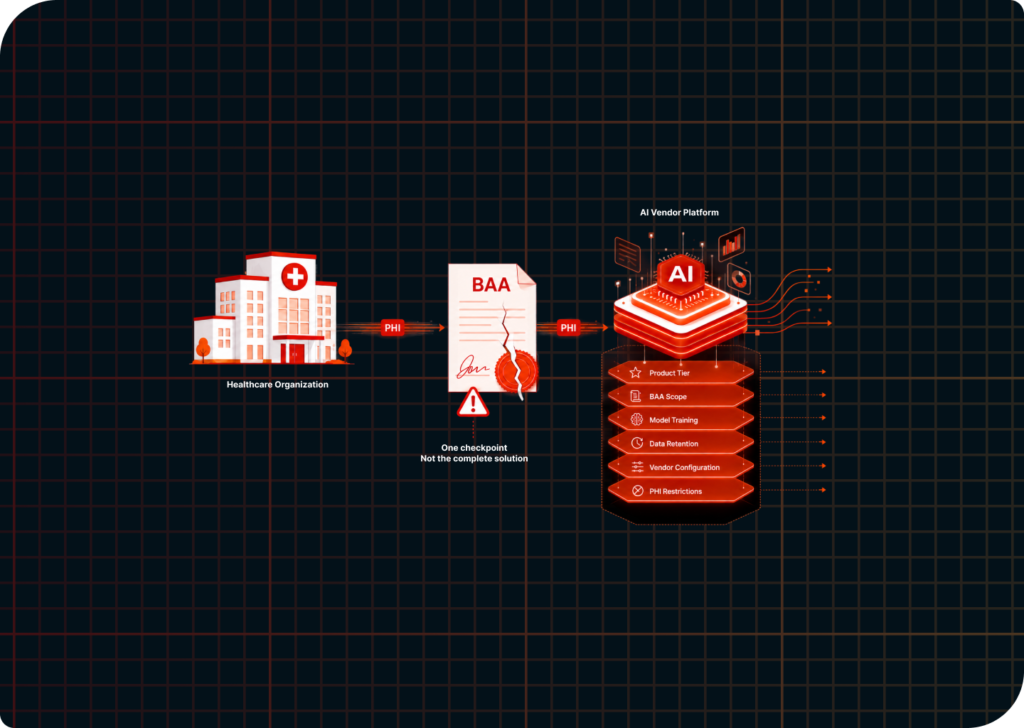
Hospitals are adopting AI faster than compliance can track. Apps like ambient scribes, diagnostic tools, and scheduling bots all touch PHI and are hence business associates. In such a scenario, BAA for HIPAA compliant AI is a must-have. And yet, just having a BAA won’t suffice anymore. In this blog, we talk about what provisions to have that make a BAA meaningful.
Practical Guide to Security Gap Analysis in Compliance
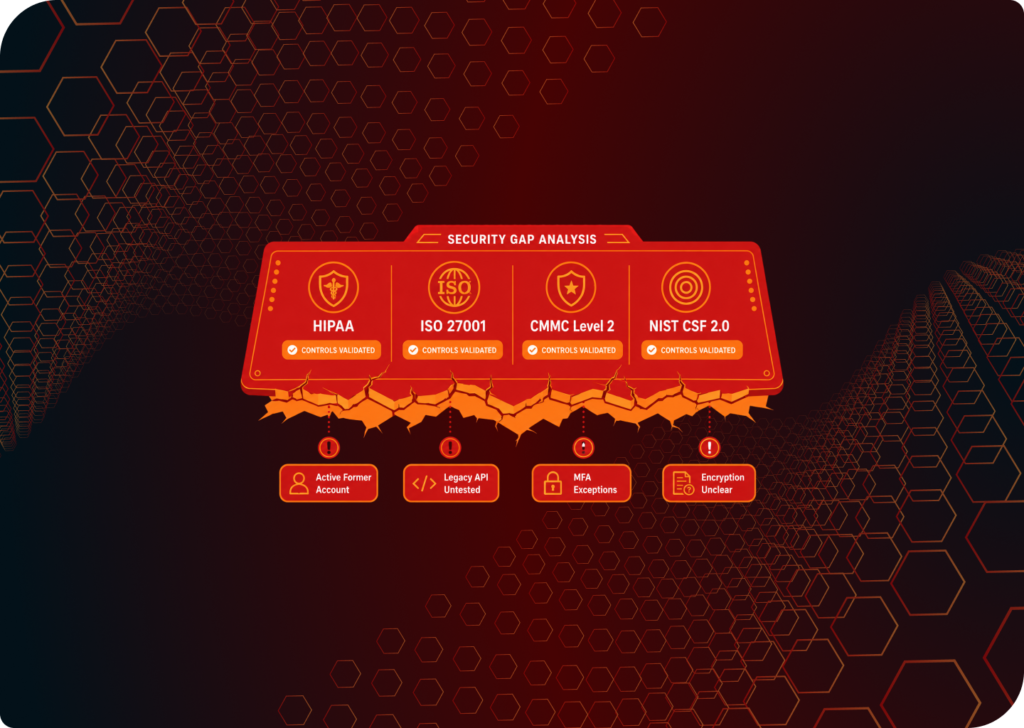
To conduct a security gap analysis, first define the assessment scope and select the applicable framework, such as HIPAA, SOC 2, or ISO 27001. Review each requirement against your existing security practices and supporting evidence. Assign maturity ratings to identify weak controls, missing processes, and documentation gaps. Then prepare a remediation roadmap outlining what needs to change to reach your target maturity level. Finally, implement the required improvements and maintain evidence that the controls work in practice.
What NC Healthcare and Life Sciences Companies Need to Know in 2026
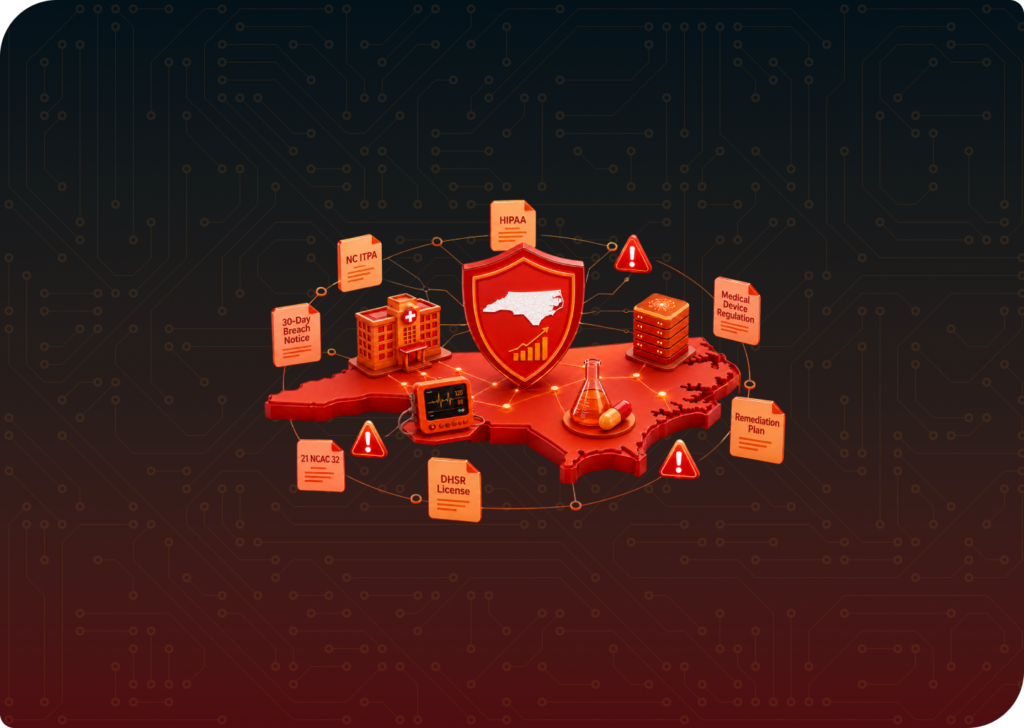
North Carolina’s Research Triangle is one of the most concentrated life sciences and health-tech corridors in the country. In 2026, it is also operating under constant cyber threats. This guide maps every compliance layer, from HIPAA and NC state law to FDA QMSR and SOC 2 and lets you know how to prioritize them.
Arizona HIPAA Compliance: What Healthtech Companies Need to Know About the 45-Day Breach Rule
Arizona constantly ranks in the Top 10 for healthcare data breaches. With 232 hospitals and one of the fastest-growing healthtech ecosystems in the nation, the state’s compliance exposure is real and underestimated. This compliance guide covers what cybersecurity in Arizona’s healthtech sector should look like.
What New York Healthcare Organizations Need to Know About Compliances
Federal HIPAA is just the starting point for New York healthcare organizations. The SHIELD Act, NYDFS 23 NYCRR Part 500, and the incoming NYHIPA each add independent obligations, enforcement timelines, and penalties that HIPAA compliance alone cannot satisfy. This blog gives a detailed look into each framework and tells you how to stay compliant.
Compliance Guide for Ohio Healthcare and Manufacturing Organizations
Ohio ranked 8th in the nation for healthcare data breaches in 2025. And across the Ohio manufacturing corridor, CMMC enforcement is currently ongoing. For SMBs operating in both sectors, this blog maps the full compliance landscape, from HIPAA and CMMC to Ohio state law, and how to build one defensible program.