
Your health app encrypts everything. Your team knows the HIPAA Security Rule cold. You’ve even built a 60-day breach plan. Great plan, but possibly the wrong rulebook.
Here’s the twist in Arizona HIPAA compliance. Many direct-to-consumer health apps aren’t covered by HIPAA at all. Arizona’s breach law, A.R.S. § 18-552, often is. It gives you 45 days to notify affected residents once you confirm a breach. Hit 1,000 people, and the Attorney General and state Homeland Security expect a call too.
By day 46, you’re not compliant, you’re explaining.
So, start with the question most founders skip, which rules actually apply to you? If you’re a covered entity or business associate, HIPAA sets your baseline. Here’s what it requires.
What Does HIPAA Require from Arizona Healthcare Organizations?
HIPAA requires Arizona covered entities and business associates to protect PHI under three federal rules, and the Security Rule carries most of the technical work. Most organizations know HIPAA exists. Far fewer have implemented it in a way that holds up to an OCR investigation.
The Three HIPAA Rules Arizona Organizations Must Meet
- Privacy Rule: Governs how you use and disclose PHI.
- Security Rule: Sets the administrative, physical and technical safeguards for electronic PHI (ePHI).
- Breach Notification Rule: Requires notice to individuals within 60 days of discovering a breach of unsecured PHI, plus notice to HHS.
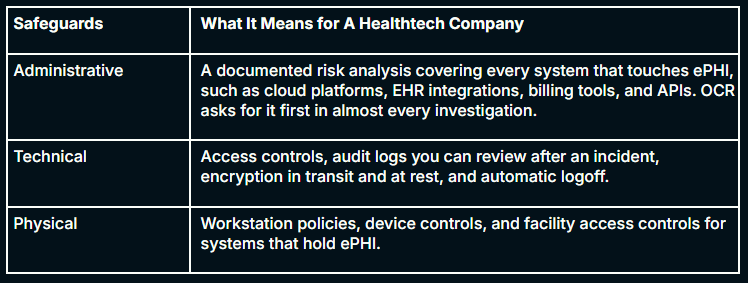
What the Security Rule Safeguards Mean in Practice
Safeguards
What It Means for A Healthtech Company
Administrative
A documented risk analysis covering every system that touches ePHI, such as cloud platforms, EHR integrations, billing tools, and APIs. OCR asks for it first in almost every investigation.
Technical
Access controls, audit logs you can review after an incident, encryption in transit and at rest, and automatic logoff.
Physical
Workstation policies, device controls, and facility access controls for systems that hold ePHI.
Where the HIPAA Security Rule Update Stands for Arizona HIPAA Compliance
The current Security Rule stays fully in force. HHS proposed an overhaul in January 2025 that would make MFA, encryption, network segmentation, annual risk analysis, and regular penetration testing mandatory. HHS has since pushed final action to July 2027.
Don’t wait for it. OCR already penalizes weak risk analysis under today’s rule, and every control in the proposal is a defensible practice now.
HIPAA is only the federal floor. Arizona adds its own rules for certain health records, and those apply to providers whether or not HIPAA does.
Which Arizona HIPAA Compliance Go Further Than Federal Rules?
Two Arizona statutes add to HIPAA for providers, one for mental health records and a stricter one for HIV-related information. Both sit on top of HIPAA rather than replacing it, so your HIPAA program needs Arizona-specific handling for these data types.
Mental Health Records Under A.R.S. § 36-509
A.R.S. § 36-509 requires health care entities to keep mental health records confidential. It allows disclosures that HIPAA’s Privacy Rule permits, so a compliant HIPAA program covers most of it.
The Arizona addition is the paper trail. When you release information to a patient’s family, friends, or others involved in their care, you must record each recipient’s name and contact details. Build that log into any care coordination or family-access feature.
HIV-Related Information Under A.R.S. § 36-664
A.R.S. § 36-664 is where Arizona clearly goes further. A general authorization to release medical records does not cover HIV-related information. The authorization must state that it is specifically for HIV-related information, and recipients can’t redisclose it except as the statute allows.
For healthtech platforms, that means separate consent flows and data tagging for HIV-related fields. One generic release form won’t satisfy Arizona law.
Substance Use Disorder Records: The Federal Overlay
SUD treatment records fall under 42 CFR Part 2, a federal rule stricter than HIPAA. Its updated rule, aligned more closely with HIPAA, reached its compliance date on February 16, 2026. Arizona’s § 36-509 defers to Part 2 for these records, so Part 2 sets the standard.
These rules apply to providers and their vendors. The bigger blind spot is the Arizona healthtech companies HIPAA doesn’t cover at all.
Which Arizona Breach Notification Law Applies If HIPAA Doesn't Cover You?
If you aren’t a covered entity or business associate, two breach rules likely apply at once: Arizona’s A.R.S. § 18-552 and the FTC’s Health Breach Notification Rule. Arizona’s deadline is shorter, so it sets your working clock.
How Arizona's 45-Day Breach Rule Works Under A.R.S. § 18-552
A.R.S. § 18-552 protects Arizona residents’ personal information. Its definitions count medical or mental health treatment and diagnosis information, health insurance ID numbers, and biometric login data when combined with a person’s name.
When you suspect an incident, you must investigate promptly. Once you determine a breach occurred, the clock starts:
- Notify affected Arizona residents within 45 days.
- If more than 1,000 people need notice, also notify the three largest credit bureaus, the Arizona Attorney General and the director of the Arizona Department of Homeland Security.
- You can skip notice only if a reasonable investigation finds the breach isn’t likely to cause substantial economic loss.
The AG enforces it, with civil penalties capped at $500,000 per breach or series of related breaches.
How the FTC Health Breach Notification Rule Adds a Federal Layer
The FTC Health Breach Notification Rule covers health apps, connected devices and similar products that HIPAA doesn’t reach.
It requires notice to affected people and, for breaches of 500 or more, to the FTC within 60 days of discovery. It also counts unauthorized sharing as a breach, such as sending health data to an ad platform without consent. Penalties reach $53,088 per violation.
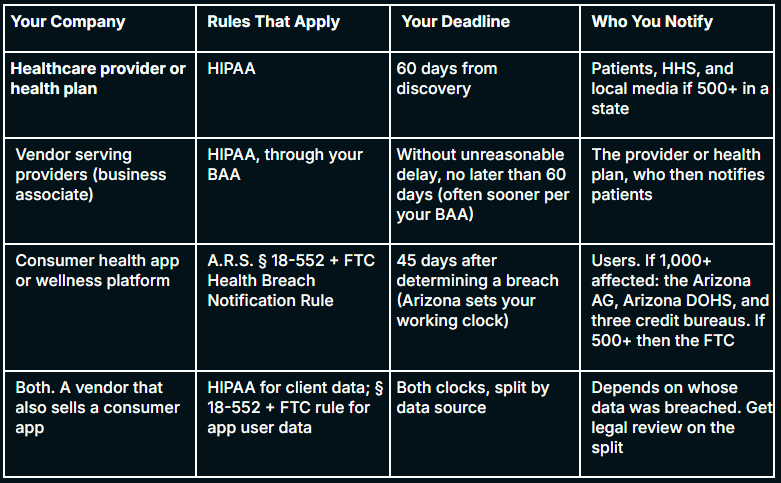
How to Tell Which Rules Apply to Your Company
Your Company
Rules That Apply
Your Deadline
Who You Notify
Healthcare provider or health plan
HIPAA
60 days from discovery
Patients, HHS, and local media if 500+ in a state
Vendor serving providers (business associate)
HIPAA, through your BAA
Without unreasonable delay, no later than 60 days (often sooner per your BAA)
The provider or health plan, who then notifies patients
Consumer health app or wellness platform
A.R.S. § 18-552 + FTC Health Breach Notification Rule
45 days after determining a breach (Arizona sets your working clock)
Users. If 1,000+ affected: the Arizona AG, Arizona DOHS, and three credit bureaus. If 500+ then the FTC
Both. A vendor that also sells a consumer app
HIPAA for client data; § 18-552 + FTC rule for app user data
Both clocks, split by data source
Depends on whose data was breached. Get legal review on the split
Once you know which column you sit in, the build steps are largely the same. Here’s how to put the program together.
How to Build an Arizona HIPAA Compliance Program in Six Steps
A defensible program maps your data, locks down vendors, implements tested controls, plans for breach clocks, validates with pentesting and trains staff on Arizona’s data types. These six steps apply whether HIPAA, Arizona law or the FTC rule governs you.
1. Run a Risk Analysis Scoped to Your Real Environment
Map every system that creates, receives, stores or sends health data such as cloud platforms, EHR integrations, billing tools, analytics services and third-party APIs. Document the threats, vulnerabilities, likelihood and impact for each.
Update it whenever you add a cloud service, integration, or product feature that touches health data. Review it at least annually, which the pending Security Rule update would make it mandatory.
2. Audit Every Vendor That Touches Health Data
If you’re a covered entity or business associate, sign a Business Associate Agreement with every vendor that can access PHI. That includes storage, analytics, and marketing platforms.
If you’re outside HIPAA, write breach-reporting terms into vendor contracts that let you meet Arizona’s 45-day clock. Then check which tools receive health data. Under the FTC rule, an unconsented share with an ad platform counts as a breach.
3. Implement the Technical Safeguards Regulators Expect
Roll out MFA, role-based access, encryption in transit and at rest, audit logging and automatic logoff on every system with health data. Encryption also matters legally. Arizona’s law and the FTC rule both apply only to unencrypted data.
4. Write an Incident Response Plan with Both Breach Clocks
Name which rules apply to you, then assign an owner to each notification stream. Pre-draft notices for individuals and every regulator on your list.
For Arizona, the 45-day clock starts once you determine a breach occurred, so document when your investigation starts and ends. Run a tabletop exercise each year so the team works through the playbook before an incident forces it.
5. Validate Controls with Annual Manual Penetration Testing
Automated scans miss the logic flaws and chained exploits attackers use. Commission a manual pentest at least once a year, scoped to web apps, APIs, cloud, Active Directory and any AI features that touch health data.
Feed every finding into your risk management plan with remediation dates. That record supports your risk analysis and holds up in an OCR or AG review.
6. Train Staff on Arizona-Specific Data Types
HIPAA requires workforce training for anyone with PHI access. Add Arizona content such as logging family disclosures of mental health records, specific authorizations for HIV-related information, and Part 2 rules for SUD records.
Non-HIPAA companies should train teams on what counts as a breach under the FTC rule, especially data sharing with marketing tools.
How KLEAP Helps Arizona Healthtech Companies Meet HIPAA and State Law
KLEAP Cybersecurity is a boutique concierge pentesting and compliance firm for healthcare and healthtech SMBs. For teams working through Arizona HIPAA compliance, we start by settling which rules apply to you, whether HIPAA, or Arizona’s § 18-552, or the FTC rule, or a mix. Then we build the program around implemented controls, not documented intentions:
- Risk analyses scoped to your actual environment.
- Vendor and BAA reviews matched to the breach clocks you face.
- Incident response plans with the right regulator list, including the Arizona AG and Department of Homeland Security where they apply.
- Manual penetration testing across web apps, APIs, cloud, Active Directory and AI features that touch health data.
Every deliverable supports your risk analysis and stands up to an OCR or AG review. If you need a partner for cybersecurity in Arizona who knows the regulations and how attackers think, we’re built for that work.
Frequently Asked Question
Does Arizona’s breach law apply if my company isn’t based in Arizona?
Yes. A.R.S. § 18-552 applies to any business that conducts business in Arizona and holds Arizona residents’ computerized personal information. Your headquarters location doesn’t matter. Your users’ location does.
If we already comply with HIPAA, do we also need to follow Arizona’s 45-day rule?
Generally, no. Arizona treats covered entities and business associates that meet HIPAA’s breach notification requirements as compliant with § 18-552. The 45-day rule mainly bites companies outside HIPAA.
How fast must a vendor tell us about a breach in Arizona?
Within 10 days of discovering it. A vendor that maintains data on your behalf must notify you, the data owner, in that window, and your own 45-day obligation keeps running.
Does Arizona’s breach law cover paper records?
No. § 18-552 covers computerized personal information only. HIPAA’s Breach Notification Rule covers PHI in any form, including paper.
Can patients or users sue under Arizona’s breach notification law?
No. The Arizona Attorney General enforces § 18-552 exclusively, and the statute creates no private right of action. Class actions after breaches usually rely on other legal claims.
Is a high score from a compliance automation tool proof of HIPAA compliance?
No. Tools track documentation and configurations. OCR looks for a risk analysis scoped to your real environment and controls that hold up in practice, which is why manual penetration testing matters.